Antimalware Service Executable High CPU Fix (Windows 10/11)
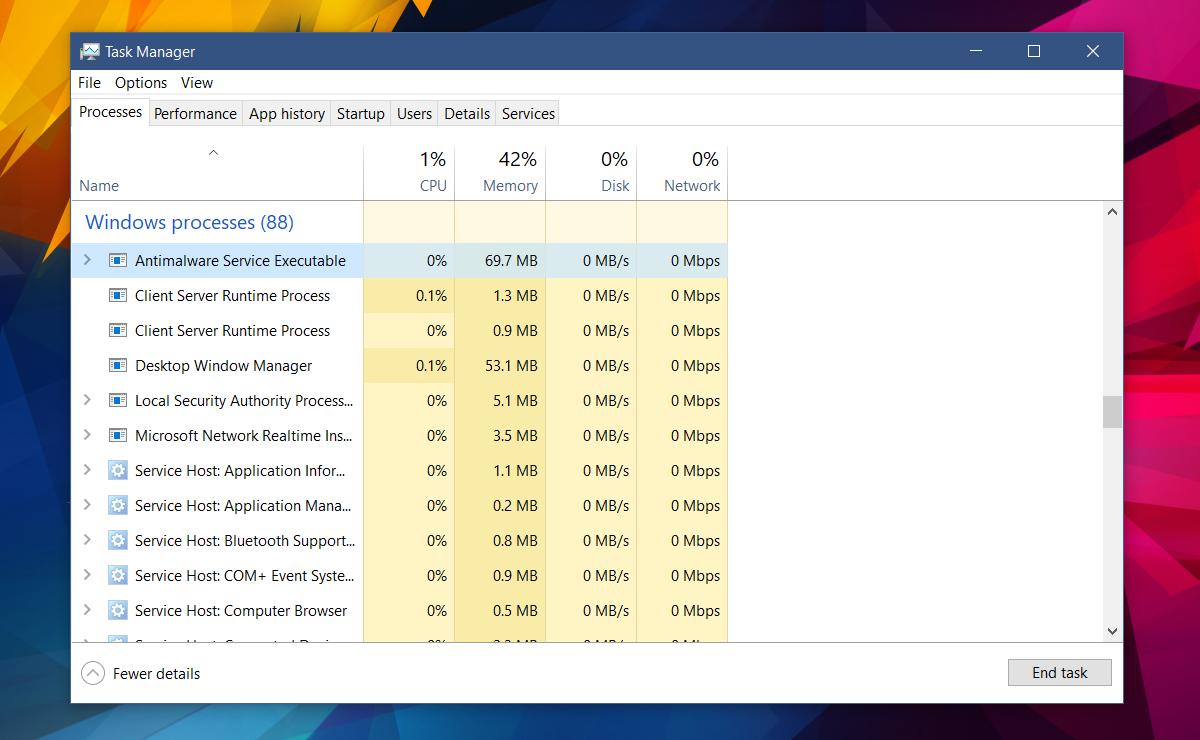
If you open Task Manager and scroll down to the Windows Processes section, you will notice a process called Antimalware Service Executable running. Understanding what is Antimalware Service Executable and why it appears in Task Manager is the first step to knowing whether it is something to worry about. For the most part, this service won’t tax your system’s resources. It consumes little, if any, memory and has no real toll on CPU usage. On occasion though, you might notice this service suddenly starts consuming more system resources. This happens when your system is idle — for example, when you’re reading something in your browser. The increased system usage lasts a short while and then returns to zero. The very simple answer: it’s Windows Defender.
What Is Antimalware Service Executable and What Does It Do?
Windows Defender runs constantly in Windows 10. It stays passive until you do something like download a file. It will scan the file for threats and then return to its dormant state. This happens until your system isn’t being used — for example, when you’re reading something online. If needed, Windows Defender will use this idle time to run a routine scan. You might have noticed that you get regular Windows Defender summary alerts. The Antimalware Service Executable process is just that: Windows Defender running.
More specifically, Antimalware Service Executable is the process name in Task Manager for MsMpEng.exe, the core engine behind Microsoft Defender Antivirus. It is responsible for several key tasks: real-time protection that monitors files and processes as you use your PC, on-access file scanning when you open or download files, scheduled background scans, and downloading and installing Defender definition updates.
Because of all this, brief spikes in CPU, memory, or disk activity from this process are completely normal. You will commonly see them during a scheduled scan, right after Windows Update delivers a definition update, or when you download a large file or archive that Defender needs to inspect.
When to worry vs. when not to worry: A temporary spike that settles down after a few minutes is almost always harmless — Defender is just doing its job. You should pay closer attention if the high resource usage persists for several hours without any obvious scan or update in progress, or if it spikes back to very high levels repeatedly every few minutes.
You should also be cautious if you see more than one process with a suspiciously similar name running at the same time. That last point in particular is a potential red flag worth investigating (see the verification section below).
Why Antimalware Service Executable Is Using High CPU, Memory, or Disk
Before jumping straight to disabling anything, it helps to understand the most common reasons MsMpEng.exe temporarily spikes in resource use. Most of the time there is a straightforward explanation:
- Scheduled Full Scan running in the background. By default, Defender schedules periodic full system scans. These are intentionally timed for when your PC is idle, but they can still cause noticeable CPU and disk usage while they run.
- Background scan triggered after idle time. If your PC has been sitting unused for a while, Defender may kick off a catch-up scan to cover any files it hasn’t checked recently.
- Real-time scanning of large downloads or archives. Downloading a large ZIP file, an installer, or a disk image gives Defender a lot of content to inspect at once, which can briefly spike disk and CPU usage.
- Defender definition updates. When Windows Update delivers new virus definitions, Defender processes and installs them in the background. This is usually brief but can temporarily push memory and CPU higher.
- Conflict with another antivirus. If you have a third-party antivirus installed but Defender has not properly entered passive mode, both products may be scanning files simultaneously, causing sustained high resource use.
- Corrupted Defender or system files. In rare cases, corrupted Defender components or Windows system files can cause the process to behave erratically and consume more resources than expected.
Quick decision rule: If the spike ends naturally after a scan or update finishes, it is almost certainly normal behavior and nothing needs to be done. If the high usage lasts for hours, keeps returning every few minutes, or appears alongside duplicate or strangely named processes, work through the safe fixes in the section below.
How to Check Whether Antimalware Service Executable Is Genuine
Some malware disguises itself as a legitimate Windows process by using a nearly identical name — for example, swapping a letter or adding an extra space. Before assuming the process in your Task Manager is the real Antimalware Service Executable, it takes less than a minute to verify it.
- Open Task Manager (Ctrl + Shift + Esc), find Antimalware Service Executable, right-click it, and choose Open file location.
- The genuine MsMpEng.exe should be located in a path such as
C:\ProgramData\Microsoft\Windows Defender\Platform\<version>\orC:\Program Files\Windows Defender\. Any other location — such as AppData, Temp, or Downloads — is a serious warning sign. - In File Explorer, right-click MsMpEng.exe, select Properties, and go to the Digital Signatures tab. The signer should be Microsoft Corporation. A missing or different signature means the file is not legitimate.
Warning signs to watch for: more than one process with a similar-looking name running at the same time, a file path pointing to a user folder like AppData or Temp, or a process name that looks almost right but has a subtle difference (extra characters, different spacing, or a lookalike letter).
If anything looks off, do not try to end the process manually. Instead, boot into Windows Security > Virus & threat protection > Scan options and run a Microsoft Defender Offline scan, then follow up with a second-opinion scanner such as Malwarebytes Free.
How to Reduce Antimalware Service Executable Usage Safely
If you have confirmed the process is genuine but resource usage is consistently higher than expected, try these steps in order before considering any drastic changes.
1. Check whether a scan or update is already in progress. Open Windows Security (search for it in the Start menu) and go to Virus & threat protection. If a scan is running, let it finish — usage will drop on its own.
2. Reschedule scans to a more convenient time. Open Task Scheduler (search for it in the Start menu), then navigate to Task Scheduler Library > Microsoft > Windows > Windows Defender. Double-click Windows Defender Scheduled Scan, go to the Triggers tab, and edit the schedule so it runs at a time when you are not actively using the PC — overnight, for example.
While you are here, also check the Windows Defender Cache Maintenance, Windows Defender Cleanup, and Windows Defender Verification tasks and reschedule any that are set to fire at inconvenient times.
3. Update Defender definitions and Windows. Outdated definitions can sometimes cause Defender to work harder than necessary. Go to Windows Security > Virus & threat protection > Protection updates and click Check for updates. Also run Windows Update and install any pending patches.
4. Confirm no two antivirus products are conflicting. If you have a third-party antivirus installed, open Windows Security and check whether Defender shows as being in passive mode. If it is still showing as active alongside another product, uninstall one of them, restart, and check usage again.
5. Use a Clean Boot to isolate the problem. If usage remains high and no obvious cause appears, a Clean Boot can help rule out a software conflict. Type msconfig in the Start menu, go to the Services tab, check Hide all Microsoft services, then click Disable all and restart. If the issue disappears, re-enable services in batches to find the culprit.
Note: ending MsMpEng.exe in Task Manager only suppresses it temporarily — it will restart on its own. Treat that as a confirmation the process is real, not a fix.
Disable Antimalware Service Executable
If you quit the Antimalware Service Executable process from the Task Manager, it just starts up again. This is because you can’t turn Windows Defender off. Since Antimalware Service Executable is a core Windows process, it simply restarts automatically.
If you were to actually disable the process, you would effectively disable Windows Defender, which isn’t advisable. Windows Defender keeps your system safe so unless you have an antivirus to use in its stead, you shouldn’t turn it off. If you do decide to use alternative protection, consider checking out the best antivirus for Windows 10/11 options available.

If you need to turn off Defender temporarily — for example, to install software that is being incorrectly flagged — the supported method is to use the Windows Security app directly. Open Windows Security, go to Virus & threat protection, click Manage settings under Virus & threat protection settings, and toggle Real-time protection off. Windows will turn it back on automatically after a short period or after a restart, which is by design.
If your goal is to replace Defender with a third-party antivirus entirely, you do not need to manually disable anything. Installing a reputable third-party antivirus will automatically put Microsoft Defender Antivirus into passive mode, where it steps back and lets the other product take the lead. This is the cleanest and most reliable approach for most users.
For IT administrators managing corporate or domain-joined devices, Defender can also be disabled permanently through Group Policy via the setting at Computer Configuration > Administrative Templates > Windows Components > Microsoft Defender Antivirus > Turn off Microsoft Defender Antivirus.
Be aware this method is intended for managed enterprise environments running Windows Pro, Enterprise, or Education editions — it is not a universal fix for home users. On devices where Tamper Protection is enabled, policy-based and manual registry changes may be blocked or ignored entirely on current Windows 10 and Windows 11 builds.
Hide Windows Defender Icon From The System Tray
If you’re okay with the Antimalware Service Executable process running and are really just annoyed with the Windows Defender icon in the system tray, you can disable it.
Open the Settings app. Go to the Personalization group of settings. Select the ‘Taskbar’ tab. Scroll down to the Notification area section and click ‘Select which icons appear on the taskbar’.

On the ‘Select which icons appear on the taskbar’ screen, turn off the Windows Defender icon. Windows Defender will continue to run and give you summary alerts. Its icon from the system tray will be hidden.